Have you ever opened a Word document and noticed comments from another employee? Maybe you’ve received a file that still shows someone’s suggested edits, or discovered that a PDF contains information you thought had been removed. It happens more often than you might think!
Most of us focus on the information we can see in a document. Did you know, however, that files can contain additional details that aren’t immediately visible too? That includes previous edits, comments, author names, and other hidden information.
That information is called metadata, and sharing it accidentally can create serious cyber-compliance problems.
What Is Metadata?
Metadata boils down to information about information.
For example, a Word document might contain the author’s name, the date it was created, previous editing activity, and comments left by coworkers. A photograph might contain information about the device that captured it, when you took it, or even where it was taken if you had location services enabled.
Some of these details are harmless, but others can reveal information that was never intended for the recipient (or anyone else) to see.
Imagine sending a customer a proposal that still contains internal comments about pricing negotiations, or sharing a document with a vendor that reveals another customer’s name in the tracked changes. You might think you’re sending one version of a file, but the recipient could discover information you didn’t realize was included in the same file.
Mistake #1: Forgetting About Tracked Changes
Microsoft Word and similar applications allow people to suggest edits without permanently replacing the original text. This feature, commonly called Track Changes, becomes incredibly useful when several people work together on the same document.
The problem? Those changes may remain inside the file when you share it outside of that circle of collaborators.
Suppose you’re preparing a contract for a customer. Your manager reviews it and suggests removing a paragraph containing sensitive financial information. So you delete the paragraph, save the file, and email it. Unfortunately, if the deletion remains recorded as a tracked change, the recipient may still be able to view that original information.
Before sharing a final document, review and accept or reject tracked changes as appropriate. Simply hiding the markup doesn’t necessarily remove it.
Mistake #2: Leaving Internal Comments Behind
Comments make collaboration easier, but they aren’t always appropriate for outside audiences.
For example, your team might leave comments discussing customer complaints, pricing strategies, employee performance, or confidential project details. Those conversations may be perfectly acceptable internally, but sharing them with someone outside the organization is another matter entirely.
Before sending a document, check whether it contains comments that the recipient shouldn’t see. If you’re using a collaborative platform such as Microsoft 365 or Google Workspace, remember that sharing permissions may also determine whether someone can view or interact with comments.
When in doubt, ask your team which version of the document you can safely share!
Mistake #3: Assuming a PDF Is Automatically Safe
Now imagine that you finish editing a document and export it as a PDF. Your metadata must be safe now, right?
Not necessarily.
PDFs can still contain metadata, annotations, embedded files, and other information that isn’t obvious when you first open them.
There’s also a particularly dangerous mistake involving redaction. For instance, suppose you need to hide someone’s Social Security number before sharing a document, so you place a black rectangle over the number and save the PDF.
It looks hidden, but depending on how you edited the file, the original text may still exist underneath that attempt to hide it. Someone could potentially copy the text or remove the covering object.
Use an approved PDF redaction tool that actually removes the underlying information. Don’t assume that covering something makes it disappear!
Mistake #4: Sharing More Than the Recipient Needs
Here’s another common scenario: A coworker asks you for the final version of a report. Instead of exporting a clean copy, you share the original working document.
That document contains months of comments, suggested changes, internal notes, and perhaps links to other confidential files, but the final recipient only needs the finished report.
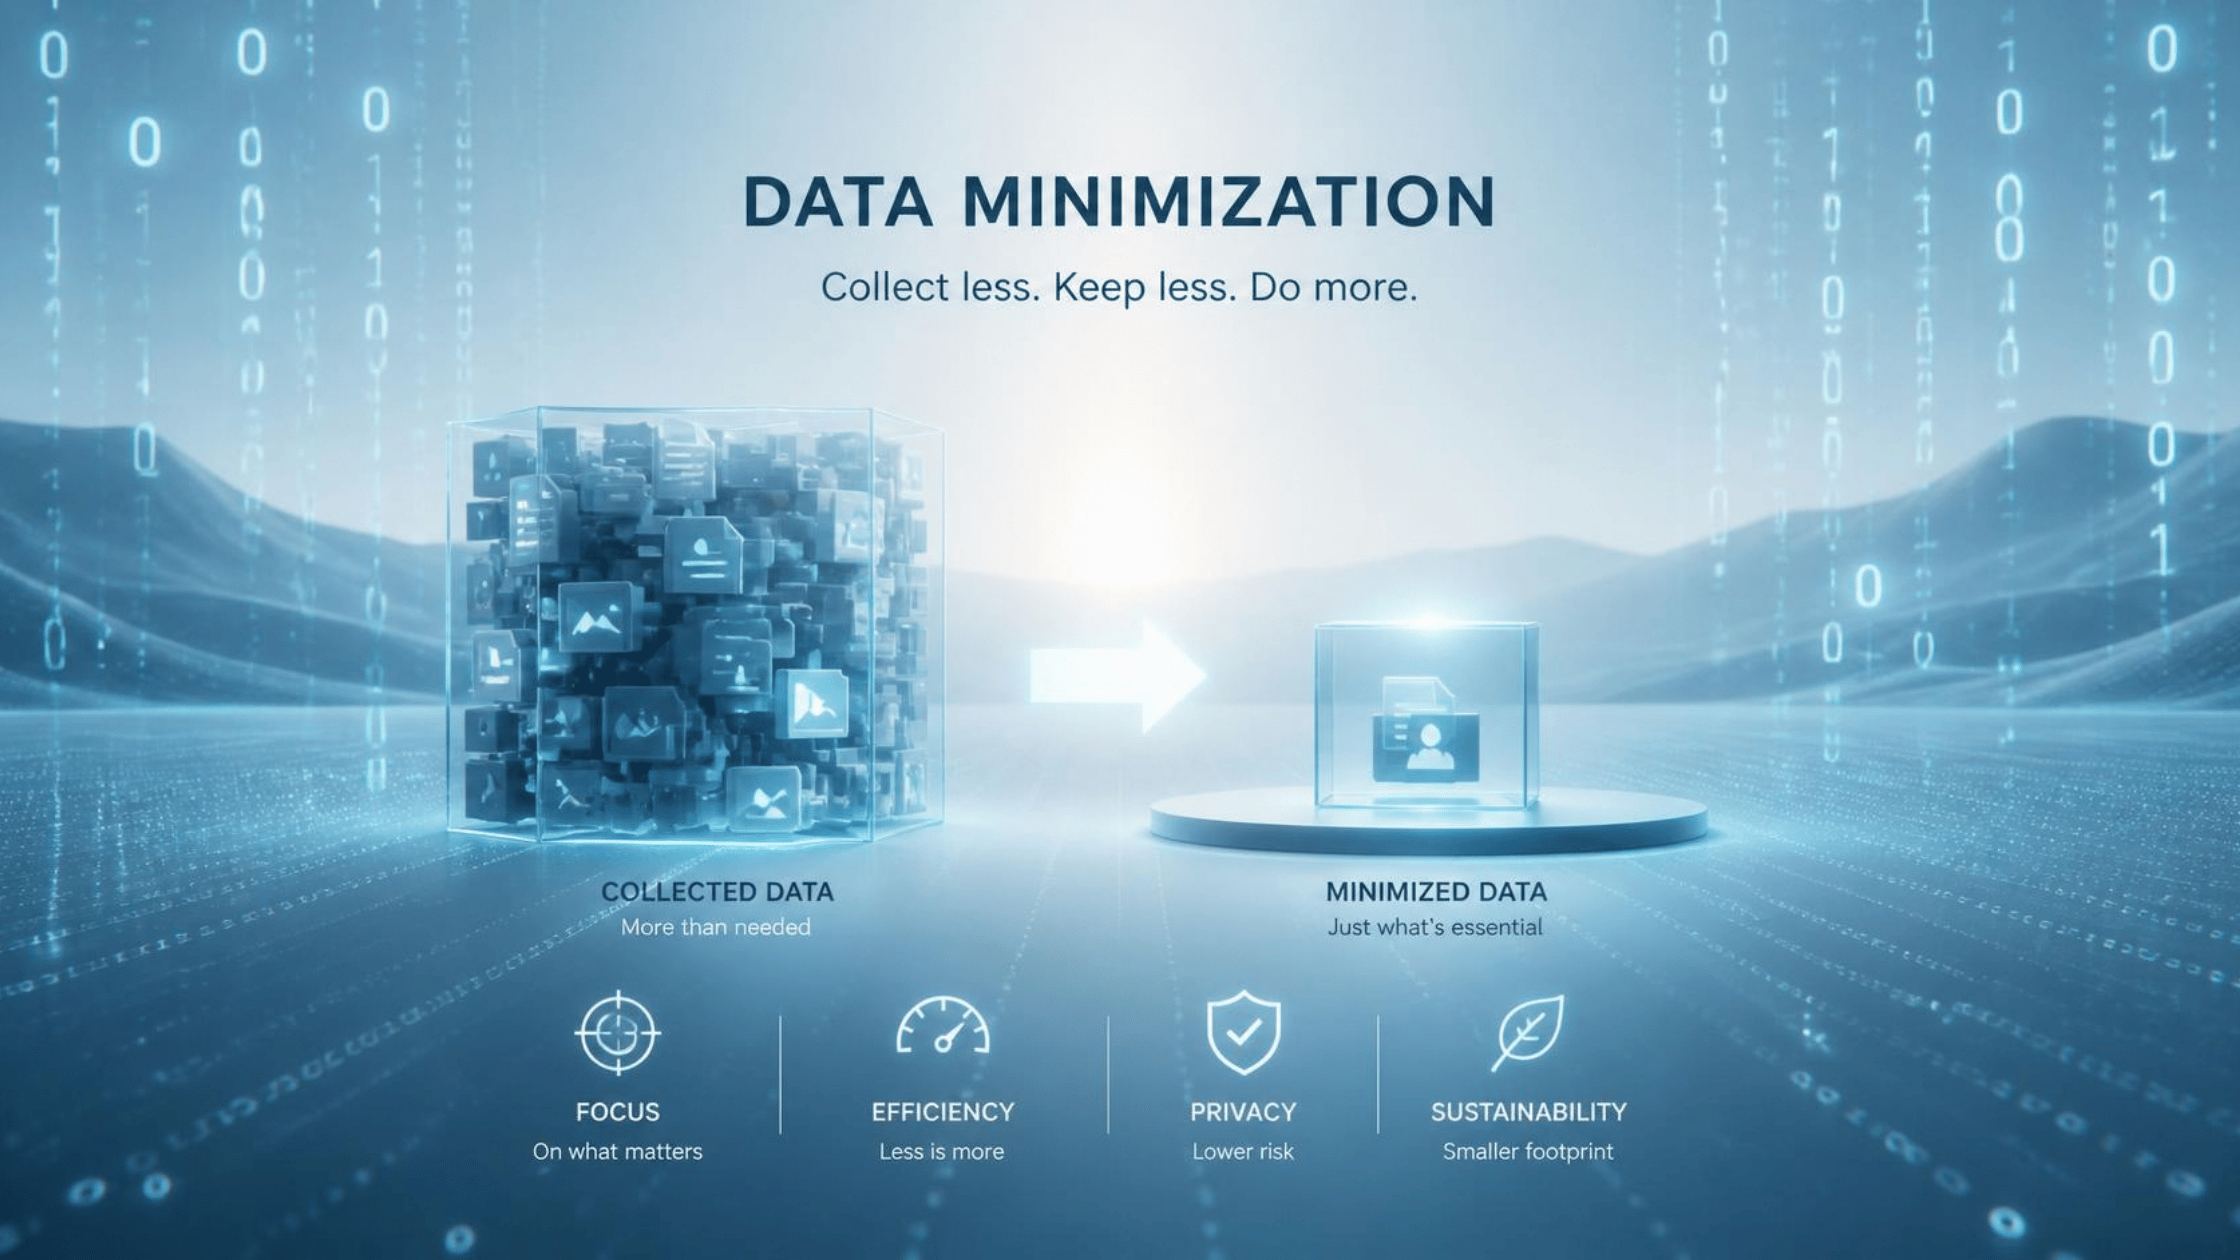
This is where the compliance principle of data minimization becomes important. The less information you have (and share), the fewer people who can be targeted by bad actors. Only share the information someone actually needs to complete their work.
If a clean, approved version of the document will accomplish the same goal, then you shouldn’t provide access to the entire editing history too.
How Can You Check a Document Before Sharing It?
Fortunately, protecting sensitive information doesn’t require you to become an expert in file formats.
You just need to build a few good habits.
Before sharing a document:
- Review comments and tracked changes. Make sure the final version doesn’t contain internal discussions or information that should remain private.
- Check document properties. Look for author information, hidden content, and other metadata using your organization’s approved tools.
- Use proper redaction tools. Never rely on black shapes or highlighting to permanently remove sensitive text.
- Confirm sharing permissions. Make sure the recipient can access only the information they’re authorized to see.
- Preview the final file. Open the exact version you plan to send and inspect it before sharing.
Some versions of Microsoft Office include a feature called Document Inspector, which can help identify hidden properties, comments, and other potentially sensitive content.
Your organization’s approved document-management tools may offer similar capabilities.
Why Does This Matter for Compliance?
Depending on your workplace, documents may contain Personally Identifiable Information (PII), Protected Health Information (PHI), financial records, or confidential customer details. Accidentally sharing that information through comments, metadata, or improper redaction can create the same kinds of privacy concerns as sending the wrong attachment.
The fact that the information wasn’t immediately visible doesn’t necessarily make the exposure less serious. If you discover that you’ve already shared a document containing sensitive information, report the mistake to your IT or security team immediately. They may be able to revoke access, replace the file, or take other steps to limit the exposure.
Most of us know to check a document for spelling mistakes before sending it. Checking for hidden information should be just as routine.
Remember that what you see on the screen isn’t always everything contained in the file. Before sharing documents, take a moment to review comments, editing history, metadata, and permissions. Use approved tools to remove information that doesn’t belong in the final version.
A document may look perfectly harmless at first glance. Taking a few extra seconds to inspect it can help ensure that you’re only sharing what you actually intended to share!